
Servers now accept tunnel peers only from their own computers (v0.46)
From v0.46, a SpanDock server's encrypted tunnel accepts only the keys of the clients and satellites it paired. What changed, what it stops and how to get it.
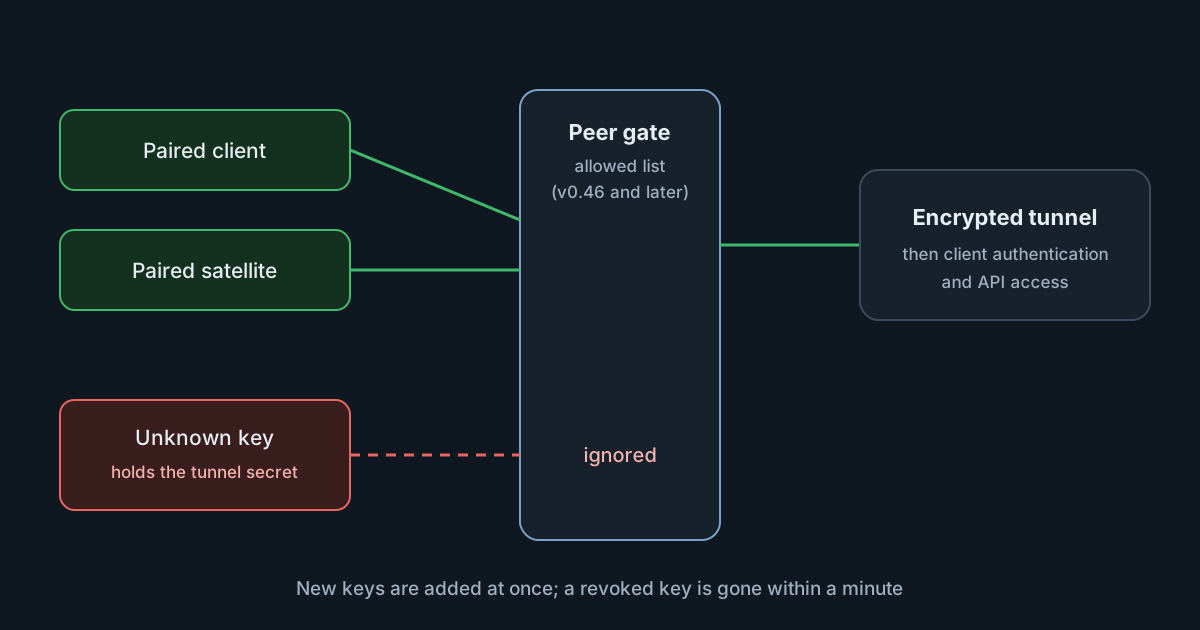
From v0.46, every SpanDock server keeps an allowed list at its tunnel's peer gate: its encrypted tunnel accepts only the keys of the clients and satellites it paired, and ignores every other key. New keys are added at once, and a revoked key is gone within a minute. To get it, update your server to v0.46 or later.
What changed
Before a computer can talk to a server over the encrypted tunnel, the server has to accept that computer's key as a peer. That decision is the peer gate, the fourth of the seven checks described in Can another company's computer reach your server?.
- Before v0.46, a server accepted any key that knew its tunnel address and pre-shared key.
- From v0.46, a server accepts only the keys of computers it paired itself. New pairings are added to the list at once; revoking a computer removes its key within a minute.
- Satellites get the list from their hub, so the same computers are accepted across a hub and its satellites.
What it stops
The case this closes is another company's computer that somehow holds your server's tunnel address and pre-shared key. From v0.46 that computer is ignored at the peer gate, before it ever becomes a peer.
Before v0.46, the same computer got through the peer gate and was stopped one step later, by client authentication: it had no valid credential for your server, so every protected route refused it. With the allowed list, it is now turned away one step earlier, at the peer gate, and client authentication still stands behind it.
Older computers
Computers paired before tunnel keys existed keep connecting through the public relay until they update. The reachability lab's model also describes a transitional state for these pairings: the allowed list exists but stays open while computers paired before SpanDock had its own relays still connect. So update the server first, and then the older computers it serves.
Who it is for
Everyone running a SpanDock server, and especially the security reviewers who ask whether another customer's computer could reach it. The allowed list is part of the server from v0.46, so updating is how you get it.
How to get it
- Update your server to v0.46 or later. Satellites receive the allowed list from their hub.
- Update computers that were paired before tunnel keys existed, so they stop relying on the public relay.
- Open the reachability lab. It now opens on v0.46 behaviour, and you can switch to the behaviour before v0.46 to compare where each kind of outsider stops.
For the full path a connection takes, read Can another company's computer reach your server? and section 3 of the security whitepaper. To make newly paired computers wait for an administrator's approval before they report, see Pairing clients.